In November 2024, my home fiber router completely choked under a 42 Gbps UDP/SYN amplification flood. All I had done was forward ports 80 and 443 on a residential IP to host a self-hosted n8n instance and a local Ollama model. Within four days of a Shodan port scan finding my open gateway, bad actors hammered the IP until my ISP blackholed my entire connection for 48 hours.
That nightmare taught me the cardinal rule of self-hosting in 2026: never open inbound router ports to the public web. The modern, zero-attack-surface architecture is Cloudflare Tunnels (Zero Trust). But setting up tunnels for production automation brings its own set of brutal gotchas—like 100-second SSE streaming drops, broken Stripe webhooks behind Access PINs, and 100MB body upload limits. Here is how to configure, harden, and debug a tunnel properly.
Why Inbound Port Forwarding is a Security Trap
Traditional port forwarding requires punching holes in your router NAT firewall. While it directs external traffic to your internal server, it broadcasts your residential or VPS IP directly onto public scan tables. Automated scanners probe for known zero-days in exposed web servers within minutes of opening port 443.
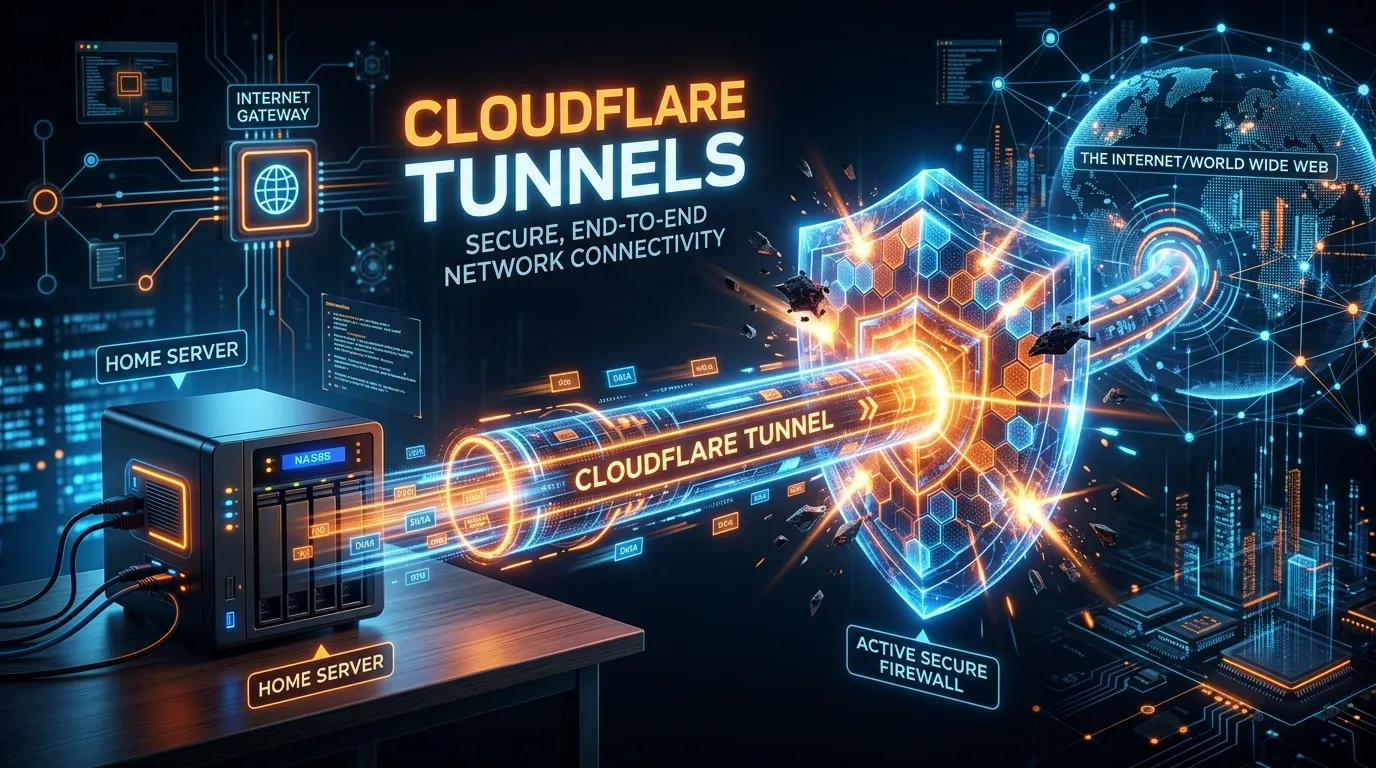
Cloudflare Tunnels completely flip this topology. A lightweight daemon named cloudflared runs inside your private network and initiates outbound-only encrypted QUIC / HTTP/2 connections to Cloudflare's Anycast edge nodes. Your firewall remains sealed (ufw default deny incoming), no ports are exposed, and your real origin IP is completely invisible to Shodan and automated DDoS vectors.
Network Architecture Breakdown: Port Forwarding vs Cloudflare Tunnels
| Vector | Standard Port Forwarding | Cloudflare Tunnels (Zero Trust) |
|---|---|---|
| Exposes Origin IP? | Yes (Direct DDoS & Port Scanning target) | No (100% Masked behind Cloudflare Anycast) |
| TLS Certificate Lifecycle | Manual Certbot renewal / HTTP-01 challenge failures | Automated Edge TLS managed by Cloudflare |
| Dynamic IP Sync | Requires brittle DDNS cron scripts | Persistent outbound socket adapts instantly |
| DDoS & Bot Mitigation | Overwhelms consumer router CPU & bandwidth | Filtered at Cloudflare 300+ Tbps edge network |
Host Your Tunnels on High-Speed NVMe Cloud VPS
Instead of risking home fiber instability, deploy your hardened Docker containers and Cloudflare Tunnels on Vultr High-Frequency servers with 10Gbps uplinks. Test your zero-trust automation stack with $300 in free trial credits.
Deploy Secure VPS with $300 Credit →Step 1: Deploy cloudflared with Docker Compose
Rather than polluting your host OS with package repositories, run cloudflared in Docker alongside your services. Here is the production docker-compose.yml:
version: '3.8'
services:
  cloudflared:
    image: cloudflare/cloudflared:latest
    container_name: cloudflared
    restart: unless-stopped
    command: tunnel --no-autoupdate run
    environment:
      - TUNNEL_TOKEN=eyJhIjoiM2...YOUR_CLOUDFLARE_TUNNEL_TOKEN_HERE
    networks:
      - proxy-net

networks:
  proxy-net:
    external: true
Production Gotcha 1: The 100-Second SSE & Streaming AI Timeout (Error 524)
If you route long-running local LLM requests (Ollama / vLLM) or streaming n8n execution nodes through a Cloudflare Tunnel, you will inevitably encounter HTTP 524: A timeout occurred after exactly 100 seconds on the free tier.
Cloudflare's HTTP proxy kills persistent HTTP sockets if no bytes are sent across the wire. To prevent drops during streaming generation, configure your config.yml with custom keepalive headers and disable buffering:
tunnel: YOUR_TUNNEL_UUID
credentials-file: /etc/cloudflared/YOUR_TUNNEL_UUID.json

ingress:
  # Route AI inference endpoint with tuned keepalive
  - hostname: ai.yourdomain.com
    service: http://ollama:11434
    originRequest:
      connectTimeout: 30s
      noChunkedEncoding: false
      keepAliveConnections: 100
      keepAliveTimeout: 90s
      tcpKeepAlive: 30s

  # Route n8n automation canvas
  - hostname: n8n.yourdomain.com
    service: http://n8n:5678

  # Catch-all
  - service: http_status:404
Production Gotcha 2: Machine-to-Machine (M2M) Webhook Lockout with Zero Trust
One of the best features of Cloudflare Zero Trust Access is putting a PIN/OAuth wall in front of your admin UI. However, if you protect n8n.yourdomain.com with an Access Policy, incoming webhooks from Stripe, GitHub, or Shopify will receive an HTTP 302 redirect to the Cloudflare login HTML page, instantly breaking all webhook integrations!
You have two ways to solve this cleanly:
- Option A — Path Bypass Policy: Create a dedicated Access Policy for
n8n.yourdomain.com/webhook/*and set the Action to Bypass (Include: Everyone). This leaves webhooks open while keeping the root UI locked. - Option B — Service Tokens: If you are connecting custom microservices, generate a Service Token in Cloudflare Zero Trust and pass
CF-Access-Client-IdandCF-Access-Client-Secretin your HTTP request headers.
Production Gotcha 3: The 100MB File Upload Limit (HTTP 413)
Cloudflare's free edge network caps incoming HTTP POST request bodies at 100MB. If your n8n workflow accepts video uploads or your local RAG pipeline ingests large document batches via multipart form-data, Cloudflare will reject the request with 413 Request Entity Too Large before it ever touches your server.
For large file ingestion pipelines, either presign S3/B2 upload URLs to let clients upload directly to storage, or use a local WireGuard / Tailscale mesh VPN to bypass Cloudflare for multi-gigabyte dataset transfers.
Summary: The Zero-Attack-Surface Architecture
By pairing Cloudflare Tunnels with strict Zero Trust Access rules and isolated Docker bridge networks, you achieve an enterprise-grade security posture on a $5/mo VPS or a local spare PC. No exposed ports, no DDNS maintenance, and no origin IP leaks.
Here is how to configure a robust Zero Trust policy:
- Log in to your Cloudflare Zero Trust Dashboard.
- Navigate to Access -> Applications on the sidebar, then click Add an Application.
- Select Self-Hosted as the application type.
- Configure the core application details:
- Application Name: Give it a clear name like
n8n Production Gateway. - Session Duration: Set this to
24 Hoursor less, depending on your strictness requirements. - Application URL: Define the exact endpoint. Subdomain:
n8n, Domain:agenticspulse.com.
- Application Name: Give it a clear name like
- Move to the Policies tab and create a new rule restricting access to specific, pre-approved identities:
- Rule Action: Set to
Allow. - Include: Select
Emailsand enter[email protected](or your personal administrative email address).
- Rule Action: Set to
- Choose your preferred identity provider. Cloudflare supports Google Workspace, GitHub OAuth, Microsoft Entra, or simple one-time PIN (OTP) emails. Save the configuration.
Now, when anyone attempts to visit n8n.agenticspulse.com, they are immediately intercepted by a secure Cloudflare login wall. The underlying server isn't even aware a request was made until the user successfully authenticates with Cloudflare. Only pre-approved users can bypass this wall to reach the actual application login portal, creating a highly resilient, multi-layered security architecture.
Advanced Security Best Practices
While Cloudflare Tunnels provide an exceptional baseline of security, you should implement these additional best practices to ensure your home server remains airtight:
- Disable SSH Password Authentication: Ensure your server only accepts SSH keys, and never passwords.
- Implement a Default Drop Firewall: Even with tunnels running, use
ufworiptablesto default-drop all incoming connections except for essential local traffic. - Enable Cloudflare WAF: Turn on the Web Application Firewall within your Cloudflare dashboard to automatically block known malicious payloads and SQL injection attempts before they enter the tunnel.
- Monitor Access Logs: Regularly review your Zero Trust access logs to identify any repeated failed login attempts from unrecognized IP addresses.
Frequently Asked Questions
1. Is the Cloudflare Tunnel service genuinely free to use?
Yes. Cloudflare's core tunnel functionality (previously Argo Tunnel) is part of their Zero Trust free tier. This generous tier allows individuals and small teams to run up to 50 active tunnels on a single account without incurring any monthly charges, making it perfect for self-hosters.
2. Can I run multiple distinct applications through just one tunnel?
Absolutely. You can configure multiple public hostnames inside a single config.yml file. By defining multiple ingress rules, you can direct traffic from various subdomains (like app1.domain.com and app2.domain.com) to entirely different local service ports or even different IP addresses on your local network.
3. Do tunnels negatively affect connection latency and performance?
Because tunnels route traffic through Cloudflare's Anycast edge locations before reaching your server, they do introduce a tiny routing hop (usually 10-20ms). However, this minimal overhead is a worthwhile trade-off. In exchange, you gain global CDN caching, automatic image optimization, enterprise-grade DDoS mitigation, and complete IP masking.
4. What happens if my server loses power or restarts?
If you have configured cloudflared as a system service (using cloudflared service install) or via Docker with a restart policy, the daemon will automatically reconnect to the nearest Cloudflare edge node as soon as the server boots up and regains internet connectivity. There is no manual intervention required.
Summary: Hardened Security for Solopreneurs
By routing inbound web connections through Cloudflare Tunnels and securing sensitive endpoints with strict Zero Trust Access Policies, you completely eliminate the severe hazards associated with traditional port forwarding. This architecture grants you enterprise-level firewall capabilities, global CDN benefits, and unparalleled peace of mind, all without spending a dime.
It is undeniably the absolute standard for securing home servers, Raspberry Pi clusters, and private VPS hosting in 2026. Stop exposing your vulnerable public IP address to opportunistic scanners, encrypt your gateway, and take control of your network's perimeter today.